-
Eds Network Security Devices
The EDS1100 and EDS2100 are unique, hybrid Ethernet terminal/multiport device servers which allow remote access to and management of virtually any IT/networking equipment or edge device such a.
-
Evaluating the quality of relay protection devices
The original unstructured record data for the defect of the relay protection devices (RPDs) may contain problems influencing the data mining, and it is lack of quantitative evaluation. So the purpose of this.
-

What are some SPN optical communication devices
Optical communication, also known as optical telecommunication, is at a distance using to carry information. It can be performed visually or by using. The earliest basic forms of optical communication date back several millennia, while the earliest electrical device created to do so was the, invented in 1880.
-
What does SOE mean in relay protection devices
SOE signal: sequence of events (resolution not greater than 2ms), record the time of occurrence of events ( switch or protection action) one by one in order, this is the sequence of events record. COS signal (non-SOE): remote signal displacement (without time stamp). The widely used United Sates standard ANSI/IEEE C37. For example, unselective protection operation during a medium voltage network fault will cause an outage for an unnecessarily large number of consumers. The IEEE COMFEDE standard provides an XML-based format. Protective relays and devices have been developed over 100 years ago to provide “lastline”of defense for the electrical systems. They are intended to quickly identify a fault and isolate it so the balance of the system continue to run under normal conditions. These types of devices protect electrical systems and components from damage when an unwanted event occurs, such as an electrical. The protection and control devices in electrical equipment can be referred to by numbers, with appropriate suffix letters when necessary, according to the functions they perform.
[PDF Version]
-
Network Security Equipment Experiment
This lab manual outlines various experiments in network security, focusing on fault detection, protocol analysis, traffic measurement, threat modeling, and vulnerability assessment. Building a Cybersecurity HomeLab is an effective way to gain hands-on experience in the field. It provides a safe environment to practice and learn various cybersecurity skills without risking damage to real systems. Hardware A. This feature is known as Network Location Awareness (NLA). Why I chose it: To simulate anonymized traffic and explore secure routing configurations within a segmented lab environment. Students will utilize tools like Wireshark, Nagios, Tcpdump, and OpenVAS to analyze network behavior and security.
-
Fiber Optic Cable Line Security
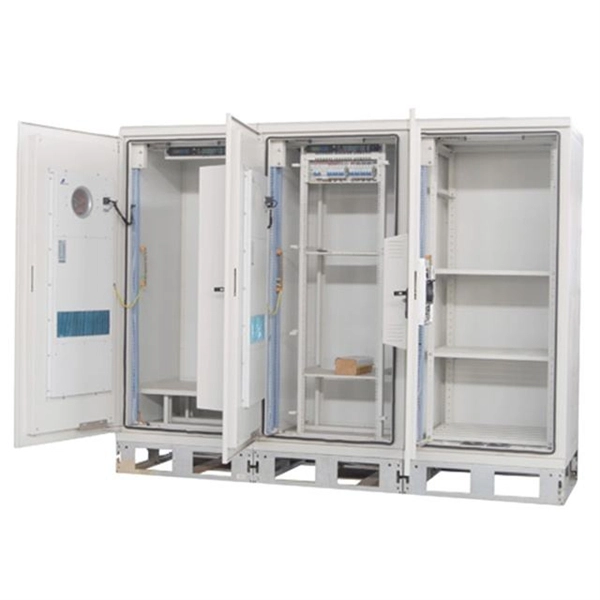
Fiber optic cables offer superior protection against electromagnetic eavesdropping compared to copper, making passive monitoring significantly more challenging. However, fiber is not invulnerable. Attackers with specialized tools can: Physically access unsecured junctions or. Future Fibre Technologies offers a comprehensive range of fibre optic intrusion detection and sensing solutions for the protection of high value assets and critical infrastructure. With this foundation in mind, let's dive into the three major applications. Network access control plays a significant role in maintaining the security of fiber optic networks, with measures. Researchers at NDSS 2026 demonstrate a covert acoustic eavesdropping attack that transforms standard FTTH telecom fiber cables into passive, undetectable listening devices invisible to RF scanners and immune to ultrasonic jammers. Security researchers from The Hong Kong Polytechnic University, The. Researchers from three universities in Hong Kong have published a paper demonstrating a method of eavesdropping through fiber-optic cables.
[PDF Version]
-
Full inspection time of relay protection devices
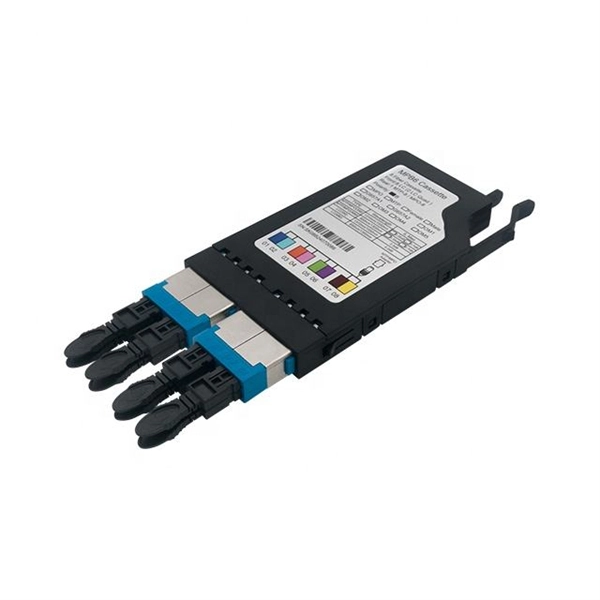
A general rule of thumb would be to visually inspect every one to two years, secondary injection testing every one to three years, and primary injection every three to five years or on major changes. Testing also needs to be done after installation, setting adjustments, or on any faults. Protection. However, the relay should be vigilant at all times. Settings of various relays need. The testing and verification of relay protection devices can be divided into four groups: Type tests are needed to prove that a protection relay meets the claimed specification and follows all relevant standards. 15 seconds in its 30+ year life. But failure to operate as intended can result in extensive damage, extended power outages, and loss of life. NETA (InterNational Electrical Testing Association) reports show 12% Failure Rates on Protective Relays Tested. Inverse time delay, on the other hand, depends on the current magnitude so, the higher the current, the shorter the delay.
[PDF Version]
-
Smart City SD-WAN Devices OSFP
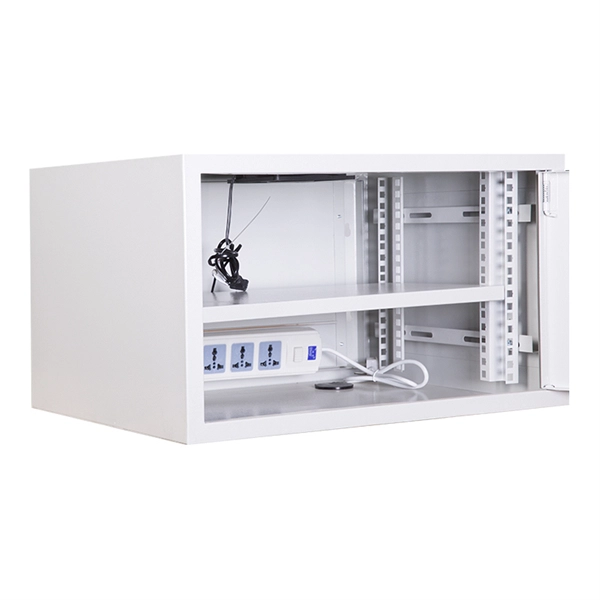
This article provides a comprehensive guide to configuring OSPF between SD-WAN edge routers and site routers across four sample sites. Each site is uniquely addressed and includes multiple loopback interfaces to emulate internal networks. This. Prisma SD-WAN supports the Open Shortest Path First routing protocol with the Layer 3 switches on the LAN at Branch and DC sites. It fully integrates routing, security, centralized policy, and orchestration into large-scale networks. In Lab 2: SD-WAN Feature Template - OSPF, participants typically delve into the configuration and optimization of SD-WAN features, with a specific focus on OSPF. Each appliance builds a route table with entries that are added automatically by the system, manually by a user, or learned from a routing protocol (SD-WAN Fabric Subnet Sharing, BGP, or OSPF). You can filter the type of routes displayed by.
[PDF Version]