-

Huawei Switch Access Security Settings
During the startup process of the switch, press Ctrl+B or Ctrl+E. In V200R019 and earlier versions, use the preset password to access the BootROM or BootLoad menu, and change the BootROM or BootLoad password. Console ports, also called serial ports, are physical interfaces. Open Terminal (macOS/Linux) or PuTTY (Windows), set baud rate to 9600. Connect to the device using SSH or the console port Log in to the management interface using your username and password. Use the following AAA commands to create a new user. For example: Replace USERNAME with the new username, set the password, define service-type (telnet, ssh, etc. ), and specify. 🔊 Welcome to our Huawei Networking Tutorial Series! 🎓 Enhance your network security with Access Control Lists (ACL) on Huawei switches!🔐 In this tutorial, you'll learn how to configure Access Control List (ACL) on Huawei Devices quickly. It can be used to. This document describes the CLI-based configurations of universal protocols and common features for Huawei switches on basic networks.
[PDF Version]
-
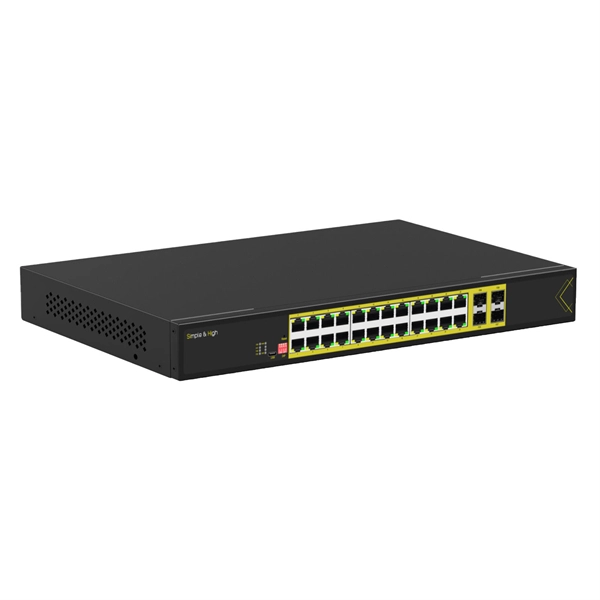
Huawei 1720 Fiber Optic Switch
Huawei S1720-10GW-PWR-2P switch with 8xGE PoE+ ports, 2xGE SFP uplinks and 124W PoE for small enterprise access networks. With 16 GE ports, 2 GE SFP ports, and 2 combo ports supporting 10/100/1000 or SFP, this switch provides flexible connectivity for office networks, workgroups, and branch. Huawei S1700 series switches are ideal for small to medium-sized businesses, Internet cafes, hotels, schools, and others. They are easy to install and maintain and provide rich services, helping customers build secure, reliable, and high-performance networks.
-
Three-layer architecture without access switch
Collapsed Core Architecture is a campus network design wherein we combine the core and distribution layers. The core and distribution functions are implemented by a single device. In this discussion, let's break down three major network architectures—Two-Tier, Three-Tier, and Spine-Leaf—using simple language and real-world examples to help you pick the best fit for your needs. Access Layer – Access switches connect end devices to the network. But this is a. Whether you are studying for the Cisco CCNA or CCNP Enterprise certifications, or designing a production network for a real organization, the three-tier hierarchical model is one of the most foundational architectures you will ever work with. Three-Tier Hierarchical Architecture.
-
Core Access Layer 2 Switch
The layer 2 switches prevent over-crowding of data packets in transmission links and access devices. Distribution Layer: The distribution layer is an intermediate layer. Introduction: The Hierarchical Network Model In today's complex IT environments, network design follows a structured approach to ensure. The term campus LAN refers to a LAN network that spans a single geographic location, such as a building or university campus. An enterprise network is a large network that may contain several campus networks spanning different. In enterprise networking, the hierarchical three-tier model is divided into three distinct roles: access switches (which connect end-user devices to the network via Layer 2), distribution switches (which route inter-VLAN traffic and enforce security policies at Layer 3), and core switches (which. Function: Connection point for all devices on a segment of segment of a network that breaks down and absorbs the data flow between all of the connected devices rather than flooding it to all connected devices.
[PDF Version]
-

Switch Access Authentication Steps
switch (config)# aaa accounting Configure the accounting service on the device. 1X (Port Based Network. If you configure an SDM template and then perform the show sdm prefer command, the template currently in use displays. You should have access to and should configure a RADIUS server before. Selects the type of security access: local Authenticates with the manager and operator password you configure in the switch. 1X port-based authentication on Cisco switches. 1X, MAC RADIUS, or captive portal. Authentication prevents unauthenticated devices and users from gaining access to your LAN.
-

Access Switch Connection AP Port Mode
The topic Configuring Wired Port Profiles on APs covers the configuration of wired port profiles for access points running AOS 10. Example configuration of an access wired port profile applied to an AP's configuration: switchport-mode access allowed-vlan all. hi everyone, is there a place online where i can find the recommended port configurations for Access Points in Cisco switches? I am taking over / cleaning up a giant network and I'd really to get things to best practices. The persona of an AP's Ethernet port determines how the port is used, where the port connects, and what type of traffic is. As Wi-Fi becomes the foundation of digital transformation, businesses and households need to optimize their wireless infrastructure. The AP modes can either be client-serving or are used for network management. What are Access Point Modes and Their Significance? Wireless APs can operate in multiple modes. Each mode is designed for a particular scenario. 2 Questions about AP mode: 1. 2022-12-13 21:39:17 - last edited.
[PDF Version]
-

Core Switch Aggregation Layer Access Layer
The aggregation or distribution switches are the intermediary layer between the core and access layers. The lowest tier is the access layer, which is used to connect all of the various end devices, such as PCs, printers, and other network components such as routers or access. Function: Connection point for all devices on a segment of segment of a network that breaks down and absorbs the data flow between all of the connected devices rather than flooding it to all connected devices. Together, these layers can offer consumers a network that is safe, reliable, and affordable. The main responsibility of these.
-

Configuration of Aggregation Access Switch
Configuration involves setting up VLANs, QoS policies, security rules, and routing protocols. This process typically requires technical expertise and a thorough understanding of networking concepts. Consult the switch's documentation and consider seeking assistance from a qualified. Aggregation and access devices downstream to the core layer can automatically go online through Zero Touch Provisioning (ZTP). This section describes three automatic deployment modes, which can be selected based on the site requirements. Access switches are utilized to increase port count for layer 2 access to wired devices and access. IEEE 802. Aggregating multiple links between physical interfaces creates a single logical point-to-point trunk link or a LAG.
[PDF Version]
-
What are the full-process switch access methods
Important Switching Methods are store and forward, cut-through and fragment-free. In this article, we will understand the process switching operation, its key features and related configuration – Topics of Content In IP Routing, packet switching methods are used to address the primary function of. A switch is built similar to a computer with internal components that each are responsible to provide a certain feature. These internal components are usually refereed to as ASICs. This process is done in the software. Process. Cisco switches support a special wire-speed mechanism that processes packets at high speeds.
-

Switch controls computer access
Switch control is an assistive technology input method that enables users to control computers using one or more switches instead of traditional keyboards or mice. Let's look at some switches in action and go through how you design switch friendly interfaces. However, what do you do if you can't use these? A number of 'alternative access' systems exist, for example alternative keyboards, trackerballs, touchscreens, headpointers etc.
-

Huawei switch with 4 optical ports connected in series
CloudEngine S5736-S series switches are next-generation standard all-optical GE access switches that provide 24-port and 48-port models, and provide four 10GE ports and one extended slot(optional). Based on Huawei's Versatile Routing Platform (VRP), CloudEngine S5736-S supports enhanced Layer 3 features, simplified Operations and Maintenance. There are several S5736-S24UM4XC bundles, which consist of different power supplies and ports, as listed in Table 4-1481. By default, multi-GE ports support 100 Mbit/s and 1000 Mbit/s. You can purchase an RTU license to increase the port rate to 2. There is a label. S5735-S24P4X is the Huawei S5735-S switch with 24 x 10/100/1000BASE-T ports, 4 x 10 GE SFP+ ports, and PoE+. Non-certified optical or copper modules cannot ensure transmission reliability and may affect service stability. Huawei S5720-32P-EI-AC Switch II.
[PDF Version]
-
Aggregation Switch Access Gateway
Access Gateway mode is normally used as host aggregation. In other words, a switch in AG mode aggregates traffic from a number of host systems onto a single uplink N_Port. Similarly, many targets can be aggregated onto to a single uplink N_Port, as shown in the following. An aggregation switch is a network device that consolidates traffic from multiple access switches, wireless access points, or other edge devices and forwards it to core switches or routers. "Campus Networks Typical Configuration Examples" provides typical campus network networking modes and a variety of deployment examples. 3ad) that dynamically manages link aggregation, provides automatic failover, and helps prevent misconfigurations by ensuring both ends of the link agree on the aggregation settings. This article looks at what each such tool does, compares how they differ from each other, and offers suggestions as to what sort of network each. LANCOM aggregation switches enable high-performance and hierarchical switch infrastructures to be set up and serve as the distribution basis for networking subordinate access switches.
[PDF Version]
-

Size of Huawei S7706 Core Switch
The S7706 chassis is 10 U high (1 U = 44. Figure 4-21 and. g switches designed for next-generation enterprise networks. The S7700 design is based on Huawei's intelligent multi-layer switching technology to provide intelligent service optimization methods, such as MPLS VPN, traffic analysis, comprehensive H-QoS policies, controllable multicast, load. ei S7706 Assembly Chassis. Agile features supported in V200R005C00 and later versions 3. Innovative Cluster Switching System (CSS) 4. Left-to-rear air flow, high-density wiringThe S7700 series is available in three models: S7703, S7706, and S7712.
-

Huawei switch optical port inspection
This document describes how to check the switch interface or port status and how to locate an interface physically down fault and restore the interface to the up state. Hardware failures:. This section describes the insertion loss and reflection requirements of optical links and the method of checking the quality of optical links for the application of 50G optical modules with the PAM4 coding technology. To check if there are any packet errors and negotiation modes on ports, you can use the command display interface. During use, reading optical module information helps understand its real-time operating status, enabling faster troubleshooting of link abnormalities. Run the display transceiver [interface interface-type interface-number | slot slot-id], to view the information on.
[PDF Version]
-

Access Switch RADIUS Authentication
Configure the switch for RADIUS authentication through the following access methods: Console: Either direct serial-port connection or modem connection. Telnet: Inbound Telnet must be enabled (the default). SSH: To use RADIUS for SSH access, first configure the switch . Cisco Meraki MS switches offer the ability to configure access policies, which require connecting devices to authenticate against a RADIUS server before they are granted network access. These access policies are typically applied to ports on access-layer switches to prevent unauthorized devices. RADIUS: RADIUS is a distributed client/server system that secures networks against unauthorized access by providing flexible administrative control over authentication, authorization processes, and offers detailed accounting information. This applies the privilege level specified by the service type value received from the RADIUS server. ) radius-server no radius-server [host <ip-addresss>] Adds a. Switch functions as the network access server on the destination network, providing access to users only after they are remotely authenticated by the server.
[PDF Version]