-
Eds Network Security Devices
The EDS1100 and EDS2100 are unique, hybrid Ethernet terminal/multiport device servers which allow remote access to and management of virtually any IT/networking equipment or edge device such a.
-
Network security equipment mainly refers to
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. They include firewalls, intrusion prevention systems, VPN gateways, and other tools that safeguard data across network. Network security devices provide automated functionality that can help stop network-based cyberattacks. A key strategy in network security is the multi-layered defense. Network security covers many technologies, devices, and processes. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. While networking security tools have traditionally been implemented as on-prem network security hardware or virtual appliances, in recent years many vendors and business customers have transitioned to cloud based solutions.
[PDF Version]
-
Introduction to Network Security Device Functions
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. They include firewalls, intrusion prevention systems, VPN gateways, and other tools that safeguard data across network. Network security devices provide automated functionality that can help stop network-based cyberattacks. What Are Network Security Devices? Network Security. Networking devices play a crucial role in cybersecurity, ensuring secure communication, traffic filtering, and threat prevention. Sandboxing Sandboxing runs files or code in an isolated. This guidance provides an introduction to the key topics to consider when designing, maintaining, or using networks that need to be secure and resilient.
[PDF Version]
-
Network Security Equipment Experiment
This lab manual outlines various experiments in network security, focusing on fault detection, protocol analysis, traffic measurement, threat modeling, and vulnerability assessment. Building a Cybersecurity HomeLab is an effective way to gain hands-on experience in the field. It provides a safe environment to practice and learn various cybersecurity skills without risking damage to real systems. Hardware A. This feature is known as Network Location Awareness (NLA). Why I chose it: To simulate anonymized traffic and explore secure routing configurations within a segmented lab environment. Students will utilize tools like Wireshark, Nagios, Tcpdump, and OpenVAS to analyze network behavior and security.
-
ODM Network Security Equipment OSFP
The ODM 400G OSFP SR4 transceiver module is an exceptional choice for high-quality networking equipment, delivering outstanding performance and reliability essential for modern data centers. Its compatibility with various high-speed applications ensures seamless integration into. Networking equipment for hyperscalers like Google, Amazon, Microsoft, Oracle, Meta, and others is a mix of in‑house engineering and partnerships with specialized vendors. The company's success spans across 60 countries, and IDC ranks it first in Wi-Fi 6. OSPF is an interior gateway routing protocol that uses link states rather than distance vectors for path selection. OSPF propagates link-state advertisements rather than routing table updates. Because only LSAs are exchanged instead of the entire routing tables, OSPF networks converge more quickly. FiberMall has deployed OSFP solutions across hyperscale data centers worldwide. Our engineers have seen what works—and what doesn't.
[PDF Version]
-

Aggregator Core Switch 16 Ports
The ONV33168FM is a gigabit L2+ managed Ethernet fiber switch independently developed by ONV. It has 8*10/100/1000Base-T adaptive RJ45 ports and 8*100/1000Base-X uplink SFP fiber ports. Each port can support wire-speed forwarding. US‐16‐XG offers four RJ45 ports that support 10GBASE‐T, the standard for 10 Gbps connections using Cat6 (or higher) cabling and RJ45 connectors. The ONV33168FM has L2+ full network management function, supports. As a 10G switch with full SFP+ ports that seamlessly integrates into the Omada Software Defined Networking (SDN) platform, SX3016F allows for remote and centralized management, anywhere, anytime. CRS317-1G-16S+RM is powered by a next generation switching chip, giving you wire speed. The UniFi Switch 16 XG is a fully managed 10 Gigabit aggregation switch, delivering robust performance and intelligent L2 switching. Brief content visible, double tap to read full content.
[PDF Version]
-

Ring Network Managed Industrial-Grade Switch
PLANET TSN-6325-8T4S4X is a brand-new Industrial-grade Layer 3 Time-Sensitive Networking (TSN) Managed Ethernet Switch which features 8 10/100/1000BASE-T RJ45 ports, 4 1G/2. 5GBASE-X SFP ports and 4 10GBASE-SR/LR SFP+ ports and Layer 3 IP routing in a rugged IP30 metal case for. ORing offers a comprehensive portfolio of rugged industrial Ethernet switches, from cost-effective unmanaged and PoE models to advanced Layer 2/3 managed switches enabling precise control. Our switches can address connectivity needs in a variety of vertical markets. With complete support of Ethernet Redundancy protocol, O-Ring (recovery time < 10ms over 250 units of connection).
-

Height and Dimensions of Network Cabinets
Common heights in data centers are 42U, 45U, or 48U. In high-density environments, heights can be customized up to 58U. Depth is crucial for accommodating equipment. The interior height, which is important for usability, is measured in U (height unit) in an internationally standardized way. Some standard dimensions have become. Get a comprehensive guide on server rack cabinet sizes and dimensions.
FAQs about Height and Dimensions of Network Cabinets
What is the width and depth of a server rack?
The standard width for a server rack is 19 inches, the most common size for rack-mounted IT equipment. The depth of server racks can vary, typicall...
What size is a server rack cabinet?
Server rack cabinets come in various sizes, but the standard width is usually 19 inches. The height is measured in rack units (U), typically 24U, 4...
What is the size of a standard rack unit?
A standard rack unit, abbreviated as "U," is 1.75 inches (44.45 mm) tall. This unit of measurement is used to describe the height of equipment inte...
What are the dimensions of a 42U rack?
A 42U rack typically has a height of 73.5 inches (approximately 186.69 cm), as each U is 1.75 inches. The standard width is 19 inches, and the dept...
-
How many devices does a three-level distribution box support
Each switch box shall connect to and control only one associated piece of electrical equipment (including sockets). After stepping down the voltage through the transformer's low-voltage side (0. 4kV), power distribution is achieved through three levels of distribution boxes: the main distribution board, secondary distribution boards, and tertiary distribution boards. Main Distribution Board Serves as the primary. Connects to end-use equipment via switch boxes, forming a three-tier power distribution system. A feeder usually begins with a feeder breaker at the distribution substation. This device makes sure power goes to big machines safely and quickly. Big buildings with many floors.
-
Which is better for OEM network rack cabinet servers
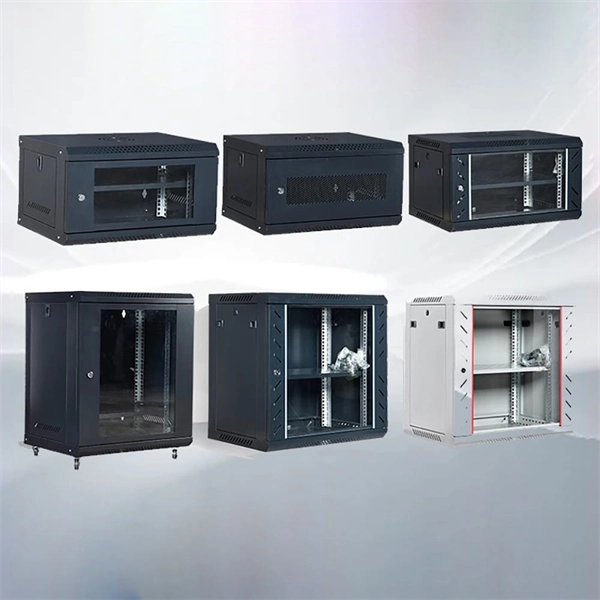
They both serve the same general purpose, holding and organizing IT equipment, but racks are often cheaper than cabinets and offer free airflow. Some people prefer cabinets for. At Weunion, we recognize that a high-performance server rack is fundamental to ensuring system uptime, thermal efficiency, and physical security. Whether you are managing a localized branch office or a massive hyperscale facility, selecting the correct enclosure is a decision that impacts your. A network rack (also called a server rack) holds networking equipment such as servers, modems, uninterruptible power supply (UPS) units, routers, network switches, and audio and video equipment. Server racks can be a specialized computer case, wall-mount rack, standing frame, or server cabinet. Choosing the right rack or cabinet is a foundational network infrastructure decision. Both types are often used to accommodate 19-inch devices (48. However, they have significant differences. This guide explains everything simply so you can pick the right one for your needs. Weight Support (Load Capacity): Crucial.
[PDF Version]
-

Scan all devices connected to the switch
Lansweeper will retrieve all relevant information from your switch like a list of network interfaces, the asset type, device description, manufacturer, model, serial number, up-time and more. Lansweeper is an Agentless Network Discovery Software that acts as a switch port mapping software and switch port discovery tool. It helps IT Professionals discover the devices that are connected to all the ports of a switch. Any advice, in the best way to go about to find this switches? How big is the facility you work at? I think I would want to walk around with a laptop and mobile phone and see where all patches go, get an idea. In a well-organized networking department, documentation should exist to allow any network engineer to quickly look up those devices that are connected to each switch port throughout the organization. There are a number of different software options that help in the process of mapping these various. With SwitchInspector you can obtain detailed information about your Cisco LAN switch and the network devices connected to it. Fast, secure, and privacy-focused with parallel Web Worker scanning.
[PDF Version]
-
What are the GPON uplink devices
A U Fiber network consists of two device types, the OLT (Optical Line Terminal), which is deployed at the provider premises, and the ONU (Optical Network Unit), which is deployed at the customer's location. An OLT can connect up to 128 ONU clients per port. GPON is an alternative to Ethernet switching in campus networking. Cisco introduces GPON with the Catalyst GPON platform. 984 is the series of standards that define the architecture and operation of gigabit -per-second–capable passive optical network (GPON). It is commonly used to implement the link to the customer (the last kilometre, or last mile) of fibre-to-the-premises (FTTP) services, using a. GPON is the reliable solution, optimizing costs while delivering exceptional broadband through Superior quality of service (QoS),dynamic bandwidth allocation capabilities and flexibility. What is GPON? GPON stands as a prominent standard in Passive Optical Network (PON), a point-to-multipoint. Example GPON topology using an ER-8-XG on the uplink side and a PLC splitter on the PON side. Here, the term 'Gigabit' in GPON denotes the maximum speed it provides which is typically 2.
[PDF Version]
-
What are the setting input values for relay protection devices
The essential parameters for relay settings include pickup voltage, dropout voltage, time delay settings, and protection thresholds. Protection relays employ a wide range of configurable parameters to identify defects & trip the breaker in a controlled & selected manner. PSM – Plug Setting Multiplier (Current Setting Multiplier) What is PSM? 2). TSM – Time. The protected zone is the part of the network in which faults cause the protection function to operate. The selection and applications of. This handbook covers the code of practice in protection circuitry including standard lead and device numbers, mode of connections at terminal strips, colour codes in multicore cables, dos and donts in execution. The goal is to strike a balance between.
[PDF Version]
-
Warranty warranty for QSFP-DD optical network switch
Providing industry-leading limited lifetime warranty. Refunds will be received about 5 business days after the receipt of returned items. Built-in Marvell DSP Chip, Max. Power Consumption 9WProduct warranty terms and other information applicable to Cisco products are available at Information about Cisco's Environmental, Social, and Governance (ESG) initiatives and performance is provided in Cisco's CSR and sustainability reporting. Power Consumption 9W Use the Compatibility Tool to verify FS. The QSFP-DD transceiver has become the standard format for 400G and 800G connections because it delivers backward compatibility and high port density and future-proofing protection which most installations need.